Not Like conventional measures that usually concentrate on specific safety instruments or isolated practices, a CSMS offers a holistic method to managing an organization’s cybersecurity dangers. Detailed specifications for the CSMS are provided within the UNR a hundred and fifty five documentation. Trendy vehicles rely on increasingly advanced electronics, software, connectivity, and autonomous capabilities, creating a rising number of potential assault surfaces. As a result, cybersecurity has turn into a crucial security and enterprise concern. ISO/SAE helps automakers, suppliers, and semiconductor corporations establish structured processes for managing these cyber risks and demonstrate due diligence throughout the availability chain. By following ISO 21434, automotive manufacturers and suppliers can show due diligence in defending autos from cyberattacks, safeguard buyer knowledge, and adjust to regulatory necessities.
Managing Quantum Safety Risks In It Hardware Lifecycles
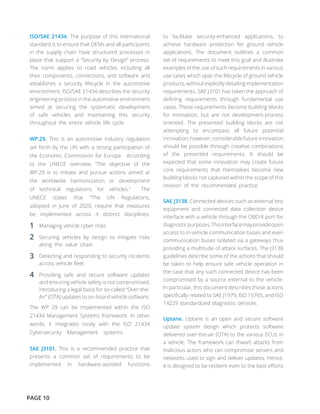
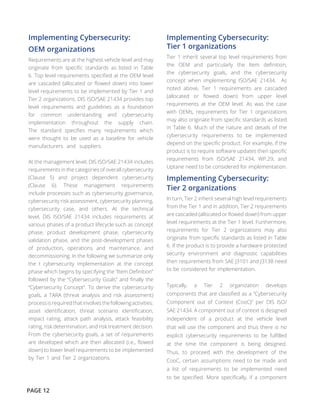
Proactive planning, cross-functional collaboration, and provider alignment are key to creating safer, safer linked automobiles. Governments and automotive our bodies are introducing cybersecurity laws, such because the UNECE WP.29 framework, that effectively require compliance with standards such as ISO/SAE 21434. The standard is obligatory for Automotive OEMs and a part of the usual additionally contains the assessment of the cybersecurity capabilities of their suppliers. The distinction between VCS and ISO usually creates confusion for suppliers going through automotive cybersecurity necessities. Over the past decade, the automotive trade has undergone a large digital transformation.
Utilizing Matlab And Simulink Products For Iso 21434
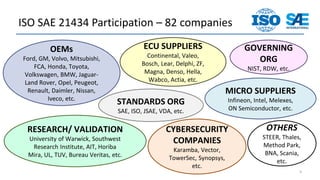
This proof contains security design critiques, safety verification plan review, privacy design reviews together with https://www.townshipliquors.com/sample-business-plan.html product metrics such as code protection stories generated by instruments just like the Synopsys Coverity. Finally, the SDL prepares the product for submit launch help by mandating requirements for post-production security controls. ISO/SAE is especially adopted by vehicle manufacturers and their suppliers of digital control items, software program, sensors and connected components.
Iso 21434 Support In Matlab, Simulink, And Polyspace
- Threat Evaluation and Risk Evaluation, or TARA, is the structured cybersecurity risk assessment strategy for automotives.
- Reaching ISO/SAE compliance requires collaboration between engineering, compliance, and supplier administration groups.
- The standard is carefully aligned with other automotive security requirements, such as ISO (functional safety), making certain a holistic method to each security and safety in automobile design and operation.
- It provides a complete framework for managing cybersecurity dangers all through the entire lifecycle of automotive methods.
- Software vulnerabilities and open source code could be exploited by hackers to compromise safety-critical systems (e.g., braking, steering), entry personal information, or even begin a automotive from a remote location.
It requires the security of hardware, software program, communication interfaces and all external techniques. In projects, implementation not often fails as a outcome of a lack of knowledge of the standard, but because of the scale and upkeep of the proof. Spreadsheet-based TARAs age shortly, high quality varies relying on the creator, and with each system change the evaluation effectively starts from scratch. This technical bulletin explains how a structured ISO/SAE development platform minimizes cybersecurity dangers and ensures highest levels of success. Participants who full the coaching are eligible to take the certification examination. Whereas these instruments assist establish and assess dangers, cybersecurity cannot rely on instruments alone.
Together, these rules set a new bar for the trade and require OEMs to reveal that their autos meet strict standards for cybersecurity and software updates. As beforehand talked about, ISO/SAE defines Risk Evaluation and Risk Assessment (TARA) to assess the cybersecurity dangers within the product. As proven in Determine 2, the four elements that aid in determining the chance rating are risk scenario, impression of the menace on the product, assault path, and the feasibility of executing the attack to score the danger. The danger score is used to make an knowledgeable determination about how the risk needs to be handled. These and other international cyber safety directives have had a significant impact on the greatest way OEMs and their suppliers develop and handle their merchandise. UNR 155 requires that OEMs implement a risk-based management framework (aka Cyber Security Management System or CSMS) for detecting potential cyber threats and defending autos towards cyber assaults.